

Latest Vault-Associate Pass Guaranteed Exam Dumps with Accurate & Updated Questions
Vault-Associate Exam Brain Dumps - Study Notes and Theory
NEW QUESTION # 11
What is a benefit of response wrapping?
- A. Ensure that only a single party can ever unwrap the token and see what's inside
- B. Log every use of a secret
- C. Provide error recovery to a secret so it is not corrupted in transit
- D. Load balanc secret generation across a Vault cluster
Answer: A
Explanation:
Response wrapping is a feature that allows Vault to take the response it would have sent to a client and instead insert it into the cubbyhole of a single-use token, returning that token instead. The client can then unwrap the token and retrieve the original response. Response wrapping has several benefits, such as providing cover, malfeasance detection, and lifetime limitation for the secret data. One of the benefits is to ensure that only a single party can ever unwrap the token and see what's inside, as the token can be used only once and cannot be unwrapped by anyone else, even the root user or the creator of the token. This provides a way to securely distribute secrets to the intended recipients and detect any tampering or interception along the way5.
The other options are not benefits of response wrapping:
Log every use of a secret: Response wrapping does not log every use of a secret, as the secret is not directly exposed to the client or the network. However, Vault does log the creation and deletion of the response-wrapping token, and the client can use the audit device to log the unwrapping operation6.
Load balance secret generation across a Vault cluster: Response wrapping does not load balance secret generation across a Vault cluster, as the secret is generated by the Vault server that receives the request and the response-wrapping token is bound to that server. However, Vault does support high availability and replication modes that can distribute the load and improve the performance of the cluster7.
Provide error recovery to a secret so it is not corrupted in transit: Response wrapping does not provide error recovery to a secret so it is not corrupted in transit, as the secret is encrypted and stored in the cubbyhole of the token and cannot be modified or corrupted by anyone. However, if the token is lost or expired, the secret cannot be recovered either, so the client should have a backup or retry mechanism to handle such cases.
NEW QUESTION # 12
Which of the following describes the Vault's auth method component?
- A. It is responsible for durable storage of client tokens
- B. It verifies a client against an internal or external system, and generates a token with root policy
- C. It verifies a client against an internal or external system, and generates a token with the appropriate policies attached
- D. It dynamically generates a unique set of secrets with appropriate permissions attached
Answer: C
Explanation:
The Vault's auth method component is the component that performs authentication and assigns identity and policies to a client. It verifies a client against an internal or external system, and generates a token with the appropriate policies attached. The token can then be used to access the secrets and resources that are authorized by the policies. Vault supports various auth methods, such as userpass, ldap, aws, kubernetes, etc., that can integrate with different identity providers and systems. The auth method component can also handle token renewal and revocation, as well as identity grouping and aliasing. Reference: Auth Methods | Vault | HashiCorp Developer, Authentication - Concepts | Vault | HashiCorp Developer
NEW QUESTION # 13
An organization wants to authenticate an AWS EC2 virtual machine with Vault to access a dynamic database secret. The only authentication method which they can use in this case is AWS.
- A. True
- B. False
Answer: B
Explanation:
The statement is false. An organization can authenticate an AWS EC2 virtual machine with Vault to access a dynamic database secret using more than one authentication method. The AWS auth method is one of the options, but not the only one. The AWS auth method supports two types of authentication: ec2 and iam. The ec2 type uses the signed EC2 instance identity document to authenticate the EC2 instance. The iam type uses the AWS Signature v4 algorithm to sign a request to the sts:GetCallerIdentity API and authenticate the IAM principal. However, the organization can also use other auth methods that are compatible with EC2 instances, such as AppRole, JWT/OIDC, or Kubernetes. These methods require the EC2 instance to have some sort of identity material, such as a role ID, a secret ID, a JWT token, or a service account token, that can be used to authenticate to Vault. The identity material can be provisioned to the EC2 instance using various mechanisms, such as user data, metadata service, or cloud-init scripts. The choice of the auth method depends on the use case, the security requirements, and the trade-offs between convenience and control. Reference: AWS - Auth Methods | Vault | HashiCorp Developer, AppRole - Auth Methods | Vault | HashiCorp Developer, JWT/OIDC - Auth Methods | Vault | HashiCorp Developer, Kubernetes - Auth Methods | Vault | HashiCorp Developer
NEW QUESTION # 14
Examine the command below. Output has been trimmed.
Which of the following statements describe the command and its output?
- A. Generated token's TTL is 60 hours
- B. Configures the AppRole auth method with user specified role ID and secret ID
- C. Generated token is an orphan token which can be renewed indefinitely
- D. Missing a default token policy
Answer: A,C
Explanation:
The command shown in the image is:
vault token create -policy=approle -orphan -period=60h
This command creates a new token with the following characteristics:
It has the policy "approle" attached to it, which grants or denies access to certain paths and operations in Vault according to the policy rules. The policy can be defined by using the vault policy write command or the sys/policy API endpoint12.
It is an orphan token, which means it has no parent token and it will not be revoked when its parent token is revoked. Orphan tokens can be useful for creating long-lived tokens that are not affected by the token hierarchy3.
It has a period of 60 hours, which means it has a renewable TTL of 60 hours. This means that the token can be renewed indefinitely as long as it does not go past the 60-hour mark from the last renewal time. The token's TTL will be reset to 60 hours upon each renewal. Periodic tokens are useful for creating tokens that have a fixed lifetime and can be easily revoked4.
NEW QUESTION # 15
The key/value v2 secrets engine is enabled at secret/ See the following policy: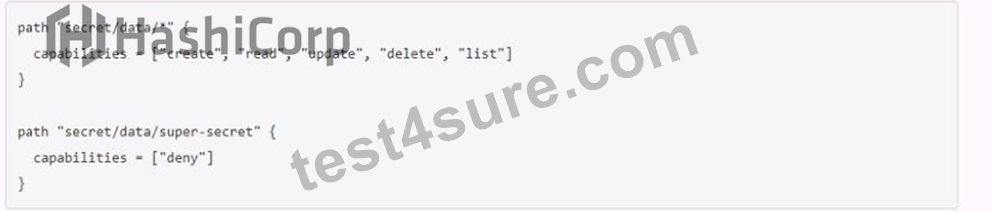
Which of the following operations are permitted by this policy? Choose two correct answers.
- A. vault kv metadata get secret/webapp1
- B. vault kv put secret/webapp1 apikey-"ABCDEFGHI] K123M"
- C. vault kv delete secret/super-secret
- D. vault kv list secret/super-secret
- E. vault kv get secret/webapp1
Answer: A,E
Explanation:
The policy shown in the image is:
path "secret/data/webapp1" { capabilities = ["create", "read", "update", "delete", "list"] } path "secret/data/super-secret" { capabilities = ["deny"] } This policy grants or denies access to the key/value v2 secrets engine mounted at secret/ according to the following rules:
The path "secret/data/webapp1" has the capabilities of "create", "read", "update", "delete", and "list". This means that the policy allows performing any of these operations on the secrets stored under this path. The data/ prefix is used to access the actual secret data in the key/value v2 secrets engine5. Therefore, the policy permits the operation of vault kv get secret/webapp1, which reads the secret data at secret/data/webapp16.
The path "secret/data/super-secret" has the capability of "deny". This means that the policy denies performing any operation on the secrets stored under this path. The policy overrides any other policy that might grant access to this path. Therefore, the policy does not permit the operations of vault kv delete secret/super-secret and vault kv list secret/super-secret, which delete and list the secret data at secret/data/super-secret respectively6.
The policy does not explicitly define any rules for the path "secret/metadata". The metadata/ prefix is used to access the metadata of the secrets in the key/value v2 secrets engine, such as the number of versions, the deletion status, the creation time, etc5. By default, if the policy grants any of the capabilities of "create", "read", "update", or "delete" on the data/ path, it also grants the same capabilities on the corresponding metadata/ path7. Therefore, the policy permits the operation of vault kv metadata get secret/webapp1, which reads the metadata of the secret at secret/metadata/webapp18.
NEW QUESTION # 16
The vault lease renew command increments the lease time from:
- A. The current time
- B. The end of the lease
Answer: A
Explanation:
The vault lease renew command increments the lease time from the current time, not the end of the lease. This means that the user can request a specific amount of time they want remaining on the lease, termed the increment. This is not an increment at the end of the current TTL; it is an increment from the current time. For example, vault lease renew -increment=3600 my-lease-id would request that the TTL of the lease be adjusted to 1 hour (3600 seconds) from now. Having the increment be rooted at the current time instead of the end of the lease makes it easy for users to reduce the length of leases if they don't actually need credentials for the full possible lease period, allowing those credentials to expire sooner and resources to be cleaned up earlier. The requested increment is completely advisory. The backend in charge of the secret can choose to completely ignore it1. Reference:
Lease, Renew, and Revoke | Vault | HashiCorp Developer
NEW QUESTION # 17
Where do you define the Namespace to log into using the Vault Ul?
To answer this question
Use your mouse to click on the screenshot in the location described above. An arrow indicator will mark where you have clicked. Click the "Answer" button once you have positioned the arrow to answer the question. You may need to scroll down to see the entire screenshot.
Answer:
Explanation:
NEW QUESTION # 18
You are performing a high number of authentications in a short amount of time. You're experiencing slow throughput for token generation. How would you solve this problem?
- A. Implement batch tokens
- B. Reduce the number of policies attached to the tokens
- C. Establish a rate limit quota
- D. Increase the time-to-live on service tokens
Answer: A
Explanation:
Batch tokens are a type of tokens that are not persisted in Vault's storage backend, but are encrypted blobs that carry enough information to perform Vault actions. Batch tokens are extremely lightweight and scalable, and can improve the throughput for token generation. Batch tokens are suitable for high-volume and ephemeral workloads, such as containers or serverless functions, that require short-lived and non-renewable tokens. Batch tokens can be created by using the -type=batch flag in the vault token create command, or by configuring the token_type parameter in the auth method's role or mount options. Batch tokens have some limitations compared to service tokens, such as the lack of renewal, revocation, listing, accessor, and cubbyhole features. Therefore, batch tokens should be used with caution and only when the trade-offs are acceptable. Reference: https://developer.hashicorp.com/vault/tutorials/tokens/batch-tokens1, https://developer.hashicorp.com/vault/docs/commands/token/create2, https://developer.hashicorp.com/vault/docs/concepts/tokens#token-types3
NEW QUESTION # 19
Your DevOps team would like to provision VMs in GCP via a CICD pipeline. They would like to integrate Vault to protect the credentials used by the tool. Which secrets engine would you recommend?
- A. Identity secrets engine
- B. Google Cloud Secrets Engine
- C. Key/Value secrets engine version 2
- D. SSH secrets engine
Answer: B
Explanation:
The Google Cloud Secrets Engine is the best option for the DevOps team to provision VMs in GCP via a CICD pipeline and integrate Vault to protect the credentials used by the tool. The Google Cloud Secrets Engine can dynamically generate GCP service account keys or OAuth tokens based on IAM policies, which can be used to authenticate and authorize the CICD tool to access GCP resources. The credentials are automatically revoked when they are no longer used or when the lease expires, ensuring that the credentials are short-lived and secure. The DevOps team can configure rolesets or static accounts in Vault to define the scope and permissions of the credentials, and use the Vault API or CLI to request credentials on demand. The Google Cloud Secrets Engine also supports generating access tokens for impersonated service accounts, which can be useful for delegating access to other service accounts without storing or managing their keys1.
The Identity Secrets Engine is not a good option for this use case, because it does not generate GCP credentials, but rather generates identity tokens that can be used to access other Vault secrets engines or namespaces2. The Key/Value Secrets Engine version 2 is also not a good option, because it does not generate dynamic credentials, but rather stores and manages static secrets that the user provides3. The SSH Secrets Engine is not a good option either, because it does not generate GCP credentials, but rather generates SSH keys or OTPs that can be used to access remote hosts via SSH4.
Reference:
Google Cloud - Secrets Engines | Vault | HashiCorp Developer
Identity - Secrets Engines | Vault | HashiCorp Developer
KV - Secrets Engines | Vault | HashiCorp Developer
SSH - Secrets Engines | Vault | HashiCorp Developer
NEW QUESTION # 20
Use this screenshot to answer the question below: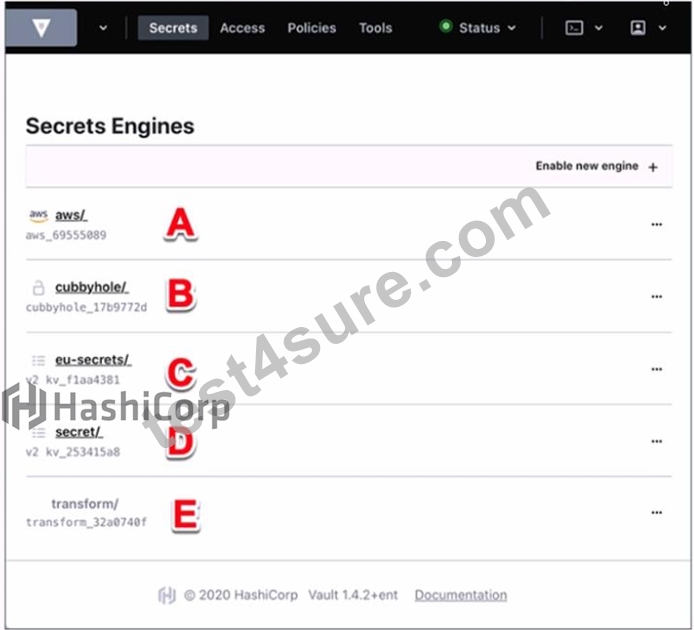
Where on this page would you click to view a secret located at secret/my-secret?
- A. B
- B. A
- C. E
- D. C
- E. D
Answer: D
Explanation:
In the HashiCorp Vault UI, secrets are organized in a tree-like structure. To view a secret located at secret/my-secret, you would click on the "secret/" folder in the tree, then click on the "my-secret" file. In this screenshot, the "secret/" folder is located at option C. This folder contains the secrets that are stored in the key/value secrets engine, which is the default secrets engine in Vault. The key/value secrets engine allows you to store arbitrary secrets as key/value pairs. The key is the path of the secret, and the value is the data of the secret. For example, the secret located at secret/my-secret has a key of "my-secret" and a value of whatever data you stored there.
Reference:
[KV - Secrets Engines | Vault | HashiCorp Developer]
NEW QUESTION # 21
You are using Vault's Transit secrets engine to encrypt your dat
a. You want to reduce the amount of content encrypted with a single key in case the key gets compromised. How would you do this?
- A. Periodically re-key the Vault's unseal keys
- B. Periodically rotate the encryption key
- C. Upgrade to Vault Enterprise and integrate with HSM
- D. Use 4096-bit RSA key to encrypt the data
Answer: B
Explanation:
The Transit secrets engine supports the rotation of encryption keys, which allows you to change the key that is used to encrypt new data without affecting the ability to decrypt data that was already encrypted. This reduces the amount of content encrypted with a single key in case the key gets compromised, and also helps you comply with the NIST guidelines for key rotation. You can rotate the encryption key manually by invoking the /transit/keys/<name>/rotate endpoint, or you can configure the key to automatically rotate based on a time interval or a number of encryption operations. When you rotate a key, Vault generates a new key version and increments the key's latest_version metadata. The new key version becomes the encryption key used for encrypting any new data. The previous key versions are still available for decrypting the existing data, unless you specify a minimum decryption version to archive the old key versions. You can also delete or disable old key versions if you want to revoke access to the data encrypted with those versions. Reference: https://developer.hashicorp.com/vault/docs/secrets/transit1, https://developer.hashicorp.com/vault/api-docs/secret/transit2
NEW QUESTION # 22
Running the second command in the GUI CLI will succeed.
- A. True
- B. False
Answer: B
Explanation:
Running the second command in the GUI CLI will fail. The second command is vault kv put secret/creds passcode=my-long-passcode. This command attempts to write a secret named creds with the value passcode=my-long-passcode to the secret path, which is the default path for the kv secrets engine. However, the kv secrets engine is not enabled at the secret path, as shown by the first command vault secrets list, which lists the enabled secrets engines and their paths. The only enabled secrets engine is the transit secrets engine at the transit path. Therefore, the second command will fail with an error message saying that no secrets engine is mounted at the path secret/. To make the second command succeed, the kv secrets engine must be enabled at the secret path or another path, using the vault secrets enable command. For example, vault secrets enable -path=secret kv would enable the kv secrets engine at the secret path. Reference: kv - Command | Vault | HashiCorp Developer, vault secrets enable - Command | Vault | HashiCorp Developer
NEW QUESTION # 23
Security requirements demand that no secrets appear in the shell history. Which command does not meet this requirement?
- A. vault kv put secret/password [email protected]
- B. vault kv put secret/password value-itsasecret
- C. vault kv put secret/password value-SSECRET_VALUE
- D. generate-password | vault kv put secret/password value
Answer: B
Explanation:
The command that does not meet the security requirement of not having secrets appear in the shell history is B. vault kv put secret/password value-itsasecret. This command would store the secret value "itsasecret" in the key/value secrets engine at the path secret/password, but it would also expose the secret value in the shell history, which could be accessed by other users or malicious actors. This is not a secure way of storing secrets in Vault.
The other commands are more secure ways of storing secrets in Vault without revealing them in the shell history.
A). generate-password | vault kv put secret/password value would use a pipe to pass the output of the generate-password command, which could be a script or a tool that generates a random password, to the vault kv put command, which would store the password in the key/value secrets engine at the path secret/password. The password would not be visible in the shell history, only the commands.
C). vault kv put secret/password [email protected] would use the @ syntax to read the secret value from a file named data.txt, which could be encrypted or protected by file permissions, and store it in the key/value secrets engine at the path secret/password. The file name would be visible in the shell history, but not the secret value.
D). vault kv put secret/password value-SSECRET_VALUE would use the -S syntax to read the secret value from the environment variable SECRET_VALUE, which could be set and unset in the shell session, and store it in the key/value secrets engine at the path secret/password. The environment variable name would be visible in the shell history, but not the secret value.
Reference:
[Write Secrets | Vault | HashiCorp Developer]
NEW QUESTION # 24
A web application uses Vault's transit secrets engine to encrypt data in-transit. If an attacker intercepts the data in transit which of the following statements are true? Choose two correct answers.
- A. Even if the attacker was able to access the raw data, they would only have encrypted bits (TLS in transit)
- B. You can rotate the encryption key so that the attacker won't be able to decrypt the data
- C. The keys can be rotated and min_decryption_version moved forward to ensure this data cannot be decrypted
- D. The Vault administrator would need to seal the Vault server immediately
Answer: A,C
Explanation:
A web application that uses Vault's transit secrets engine to encrypt data in-transit can benefit from the following security features:
Even if the attacker was able to access the raw data, they would only have encrypted bits (TLS in transit). This means that the attacker would need to obtain the encryption key from Vault in order to decrypt the data, which is protected by Vault's authentication and authorization mechanisms. The transit secrets engine does not store the data sent to it, so the attacker cannot access the data from Vault either.
The keys can be rotated and min_decryption_version moved forward to ensure this data cannot be decrypted. This means that the web application can periodically change the encryption key used to encrypt the data, and set a minimum decryption version for the key, which prevents older versions of the key from being used to decrypt the data. This way, even if the attacker somehow obtained an old version of the key, they would not be able to decrypt the data that was encrypted with a newer version of the key.
The other statements are not true, because:
You cannot rotate the encryption key so that the attacker won't be able to decrypt the data. Rotating the key alone does not prevent the attacker from decrypting the data, as they may still have access to the old version of the key that was used to encrypt the data. You need to also move the min_decryption_version forward to invalidate the old version of the key.
The Vault administrator would not need to seal the Vault server immediately. Sealing the Vault server would make it inaccessible to both the attacker and the legitimate users, and would require unsealing it with the unseal keys or the recovery keys. Sealing the Vault server is a last resort option in case of a severe compromise or emergency, and is not necessary in this scenario, as the attacker does not have access to the encryption key or the data in Vault. Reference: Transit - Secrets Engines | Vault | HashiCorp Developer, Encryption as a service: transit secrets engine | Vault | HashiCorp Developer
NEW QUESTION # 25
Which of these is not a benefit of dynamic secrets?
- A. Minimizes damage of credentials leaking
- B. Replaces cumbersome password rotation tools and practices
- C. Ensures that administrators can see every password used
- D. Supports systems which do not natively provide a method of expiring credentials
Answer: C
Explanation:
Dynamic secrets are generated on-demand by Vault and have a limited time-to-live (TTL). They do not ensure that administrators can see every password used, as they are often encrypted and ephemeral. The benefits of dynamic secrets are:
They support systems that do not natively provide a method of expiring credentials, such as databases, cloud providers, SSH, etc. Vault can revoke the credentials when they are no longer needed or when the lease expires.
They minimize the damage of credentials leaking, as they are short-lived and can be easily rotated or revoked. If a credential is compromised, the attacker has a limited window of opportunity to use it before it becomes invalid.
They replace cumbersome password rotation tools and practices, as Vault can handle the generation and revocation of credentials automatically and securely. This reduces the operational overhead and complexity of managing secrets.
NEW QUESTION # 26
Which of the following vault lease operations uses a lease _ id as an argument? Choose two correct answers.
- A. revoke
- B. describe
- C. create
- D. revoke -prefix
- E. renew
Answer: A,E
Explanation:
The vault lease operations that use a lease_id as an argument are renew and revoke. The renew operation allows a client to extend the validity of a lease associated with a secret or a token. The revoke operation allows a client to terminate a lease immediately and invalidate the secret or the token. Both operations require a lease_id as an argument to identify the lease to be renewed or revoked. The lease_id can be obtained from the response of reading a secret or creating a token, or from the vault lease list command. The other operations, revoke-prefix, create, and describe, do not use a lease_id as an argument. The revoke-prefix operation allows a client to revoke all secrets or tokens generated under a given prefix. The create operation allows a client to create a new lease for a secret. The describe operation allows a client to view information about a lease, such as its TTL, policies, and metadata. Reference: Lease, Renew, and Revoke | Vault | HashiCorp Developer, vault lease - Command | Vault | HashiCorp Developer
NEW QUESTION # 27
Which statement describes the results of this command: $ vault secrets enable transit
- A. Enables the transit secrets engine at secret path
- B. Fails because the transit secrets engine is enabled by default
- C. Enables the transit secrets engine at transit path
- D. Requires a root token to execute the command successfully
- E. Fails due to missing -path parameter
Answer: C
Explanation:
The command vault secrets enable transit enables the transit secrets engine at the transit path. The transit secrets engine is a secrets engine that handles cryptographic functions on data in-transit, such as encryption, decryption, signing, verification, hashing, and random bytes generation. The transit secrets engine does not store the data sent to it, but only performs the requested operations and returns the results. The transit secrets engine can also be viewed as "cryptography as a service" or "encryption as a service". The command vault secrets enable transit uses the default path of transit for the secrets engine, but this can be changed by using the -path option. For example, vault secrets enable -path=my-transit transit would enable the transit secrets engine at the my-transit path. Reference: Transit - Secrets Engines | Vault | HashiCorp Developer, vault secrets enable - Command | Vault | HashiCorp Developer
NEW QUESTION # 28
Which of the following is a machine-oriented Vault authentication backend?
- A. GitHub
- B. Transit
- C. AppRole
- D. Okta
Answer: C
Explanation:
AppRole is a machine-oriented authentication method that allows machines or applications to authenticate with Vault using a role ID and a secret ID. The role ID is a unique identifier for the application, and the secret ID is a single-use credential that can be delivered to the application securely. AppRole is designed to provide secure introduction of machines and applications to Vault, and to support the principle of least privilege by allowing fine-grained access control policies to be attached to each role1.
Okta, GitHub, and Transit are not machine-oriented authentication methods. Okta and GitHub are user-oriented authentication methods that allow users to authenticate with Vault using their Okta or GitHub credentials23. Transit is not an authentication method at all, but a secrets engine that provides encryption as a service4.
Reference:
AppRole Auth Method | Vault | HashiCorp Developer
Okta Auth Method | Vault | HashiCorp Developer
GitHub Auth Method | Vault | HashiCorp Developer
Transit Secrets Engine | Vault | HashiCorp Developer
NEW QUESTION # 29
An organization would like to use a scheduler to track & revoke access granted to a job (by Vault) at completion. What auth-associated Vault object should be tracked to enable this behavior?
- A. Lease ID
- B. Authentication method
- C. Token ID
- D. Token accessor
Answer: A
Explanation:
A lease ID is a unique identifier that is assigned by Vault to every dynamic secret and service type authentication token. A lease ID contains information such as the secret path, the secret version, the secret type, etc. A lease ID can be used to track and revoke access granted to a job by Vault at completion, as it allows the scheduler to perform the following operations:
Lookup the lease information by using the vault lease lookup command or the sys/leases/lookup API endpoint. This will return the metadata of the lease, such as the expire time, the issue time, the renewable status, and the TTL.
Renew the lease if needed by using the vault lease renew command or the sys/leases/renew API endpoint. This will extend the validity of the secret or the token for a specified increment, or reset the TTL to the original value if no increment is given.
Revoke the lease when the job is completed by using the vault lease revoke command or the sys/leases/revoke API endpoint. This will invalidate the secret or the token immediately and prevent any further renewals. For example, with the AWS secrets engine, the access keys will be deleted from AWS the moment a lease is revoked.
A lease ID is different from a token ID or a token accessor. A token ID is the actual value of the token that is used to authenticate to Vault and perform requests. A token ID should be treated as a secret and protected from unauthorized access. A token accessor is a secondary identifier of the token that is used for token management without revealing the token ID. A token accessor can be used to lookup, renew, or revoke a token, but not to authenticate to Vault or access secrets. A token ID or a token accessor can be used to revoke the token itself, but not the leases associated with the token. To revoke the leases, a lease ID is required.
An authentication method is a way to verify the identity of a user or a machine and issue a token with appropriate policies and metadata. An authentication method is not an object that can be tracked or revoked, but a configuration that can be enabled, disabled, tuned, or customized by using the vault auth commands or the sys/auth API endpoints.
NEW QUESTION # 30
What is the Vault CLI command to query information about the token the client is currently using?
- A. vault token lookup
- B. vault lookup token
- C. vault self-lookup
- D. vault lookup self
Answer: A
Explanation:
The Vault CLI command to query information about the token the client is currently using is vault token lookup. This command displays information about the token or accessor provided as an argument, or the locally authenticated token if no argument is given. The information includes the token ID, accessor, policies, TTL, creation time, and metadata. This command can be useful for debugging and auditing purposes, as well as for renewing or revoking tokens. Reference: token lookup - Command | Vault | HashiCorp Developer, Tokens | Vault | HashiCorp Developer
NEW QUESTION # 31
When creating a policy, an error was thrown:
Which statement describes the fix for this issue?
- A. sudo is not a capability
- B. You cannot have a wildcard (" * ") in the path
- C. Replace write with create in the capabilities list
Answer: C
Explanation:
The error was thrown because the policy code contains an invalid capability, "write". The valid capabilities for a policy are "create", "read", "update", "delete", "list", and "sudo". The "write" capability is not recognized by Vault and should be replaced with "create", which allows creating new secrets or overwriting existing ones. The other statements are not correct, because the wildcard (*) and the sudo capability are both valid in a policy. The wildcard matches any number of characters within a path segment, and the sudo capability allows performing certain operations that require root privileges.
Reference:
[Policy Syntax | Vault | HashiCorp Developer]
[Policy Syntax | Vault | HashiCorp Developer]
NEW QUESTION # 32
Vault supports which type of configuration for source limited token?
- A. Cloud-bound tokens
- B. Domain-bound tokens
- C. Certificate-bound tokens
- D. CIDR-bound tokens
Answer: D
Explanation:
Vault supports CIDR-bound tokens, which are tokens that can only be used from a specific set of IP addresses or network ranges. This is a way to limit the scope and exposure of a token in case it is compromised or leaked. CIDR-bound tokens can be created by specifying the bound_cidr_list parameter when creating or updating a token role, or by using the -bound-cidr option when creating a token using the vault token create command. CIDR-bound tokens can also be created by some auth methods, such as AWS or Kubernetes, that can automatically bind the tokens to the source IP or network of the client. Reference: Token - Auth Methods | Vault | HashiCorp Developer, vault token create - Command | Vault | HashiCorp Developer
NEW QUESTION # 33
......
HashiCorp Vault-Associate Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
Pass HashiCorp Vault-Associate Test Practice Test Questions Exam Dumps: https://www.test4sure.com/Vault-Associate-pass4sure-vce.html
The Best HashiCorp Security Automation Study Guide for the Vault-Associate Exam: https://drive.google.com/open?id=1pXYWDd0gwVZPXCs4vIFckVVsJH4OR9KX